AI Coding Sandboxes Are Not Enough. Design the Blast Radius.
Sandboxes, permissions, and allowlists matter. But serious teams also need to decide how far an AI coding agent mistake can spread.
K
Kyluke McDougallSandboxes, permissions, and allowlists matter. But serious teams also need to decide how far an AI coding agent mistake can spread.
Claude Code, Cursor, MCP tools, and similar agents are becoming more powerful. For serious product teams, the key question is no longer speed. It is control.
Hybrid and on-prem AI coding agents may unlock adoption in regulated companies. They still need architecture, boundaries, review and operational design.
MCP makes AI coding agents more useful by connecting them to tools, data and workflows. It also means teams need production-style security boundaries around those connections.
AI coding agents can accelerate schema work, migrations and backend changes. They should not be allowed near production data without clear operating rules.
AI coding agents become strategically interesting when they touch CI, pull requests, reviews and deployments. That is exactly when teams need clear operating rules.
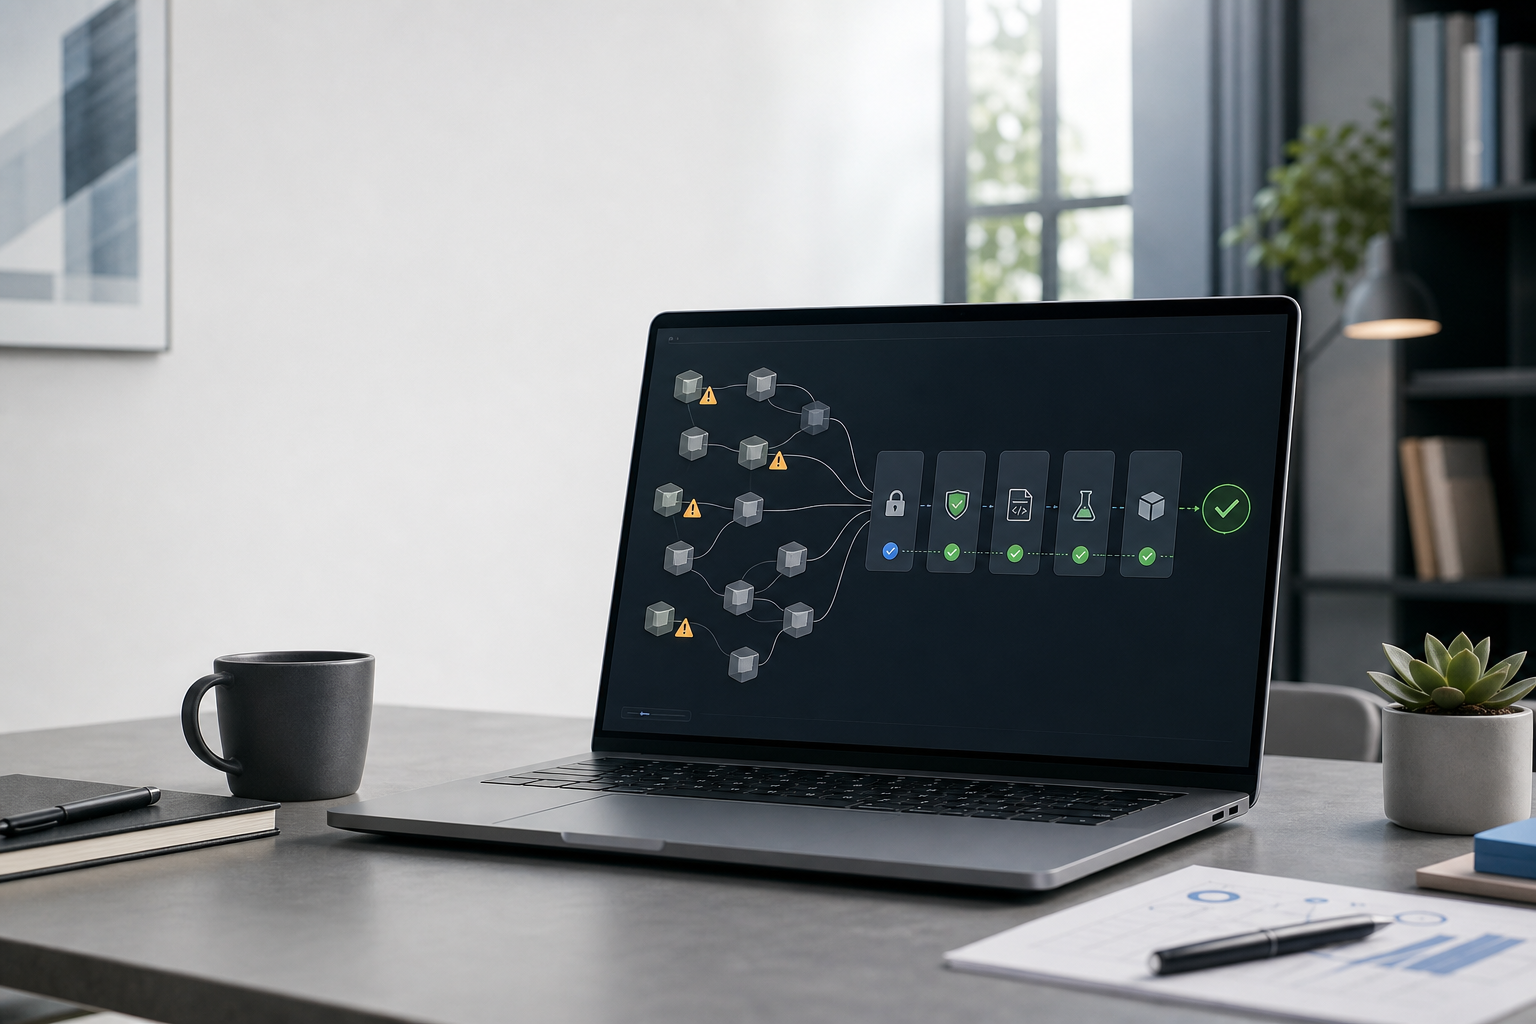
AI coding tools speed up development. They also speed up the moment when compromised dependencies, scripts and credentials become production risk.
AI coding agents are becoming part of the delivery workflow. The teams that benefit most will not be the ones that trust them blindly, but the ones that put policy, review and operational controls around them.
Pwn2Own Berlin is testing Codex, Claude Code and Cursor. For teams adopting coding agents, the lesson is clear: treat the agent runtime as privileged software, not just a smarter editor.